Select a populated tile in the detailed Risk Landscape to view the security recommendations for the assets associated with that combination of Compromise and Impact bands. Each tile represents a risk category.
Instead of listing issues for each asset individually, Compliance Manager groups assets according to the conditions they share and ranks those conditions according to the amount of risk they contribute across the selected group.
Examples of shared conditions include:
- Assets that are not protected by a hardware security module (HSM).
- Assets that use quantum-unsafe signature algorithms.
- Certificates that expire within 30 days.
Assets that are not managed through a lifecycle process.
Assets that are not compliant with policy.
Assets that are not post-quantum ready.
This approach helps identify which remediation activities could provide the greatest reduction in Compromise risk across the selected group of assets.
Recommendation details
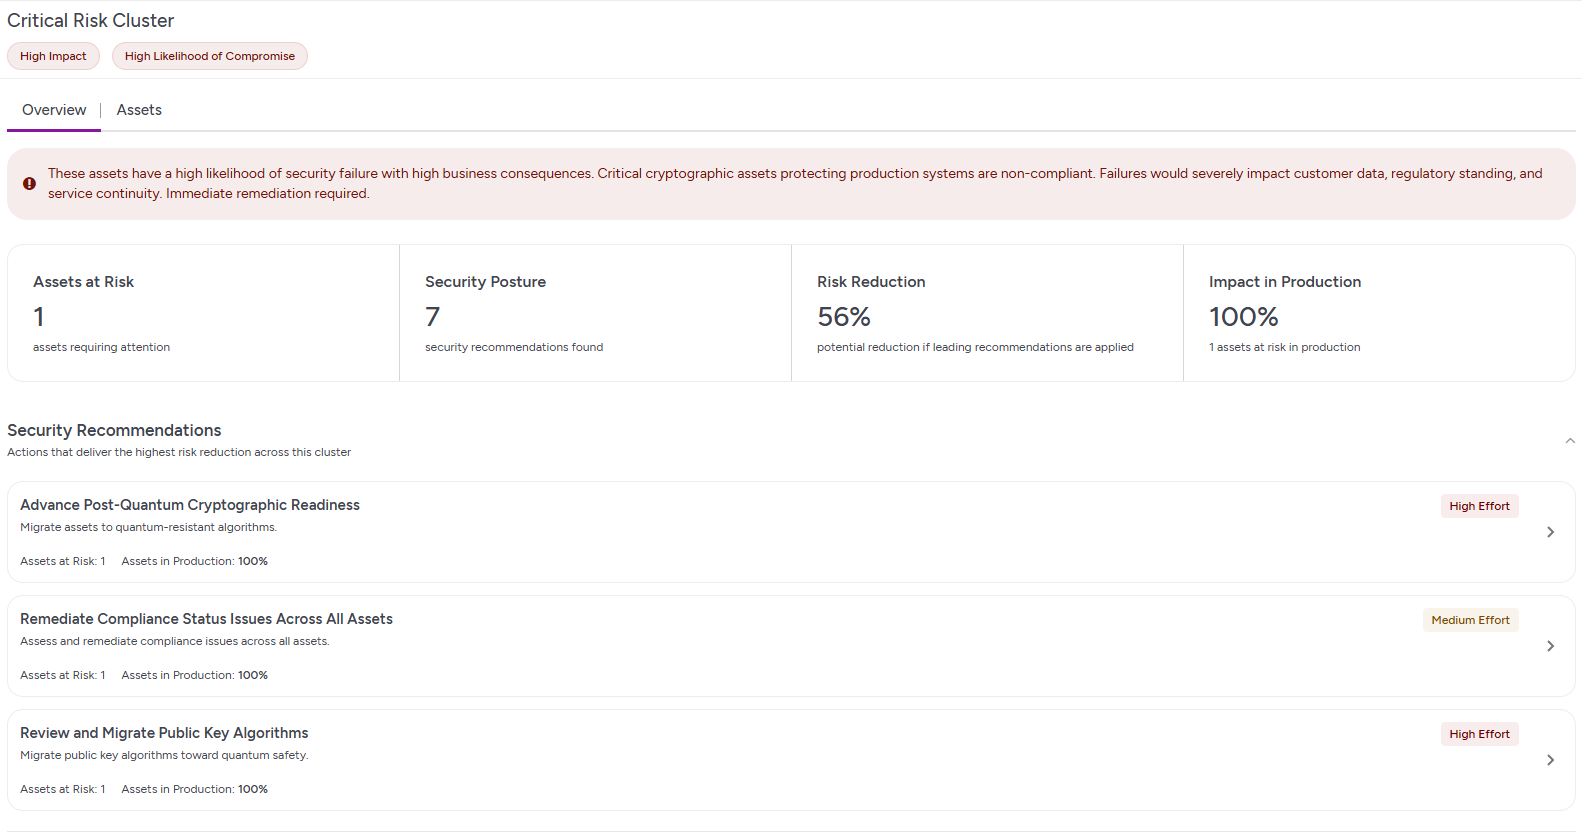
Each recommendation includes:
- A description of the issue.
Guidance on how to address the issue.
- The number of affected assets.
- The percentage of the group’s risk that could be removed.
- An indication of the required effort.
- An indication of the associated exposure.
The recommendations page also summarizes:
- The number of assets at risk.
The number of identified issues.
- The potential risk reduction available from the leading issues.
The percentage of affected assets that are in production.
Recommendations are ranked according to the amount of total risk associated with each condition. This ranking helps identify which remediation activities could provide the greatest reduction in Compromise risk across the selected group of assets.
After reviewing the recommendations, use the Business Impact section to evaluate the potential effect of implementing one or more recommendations before planning a change.
Security Recommendations for a Selected Risk Landscape Tile - Overview
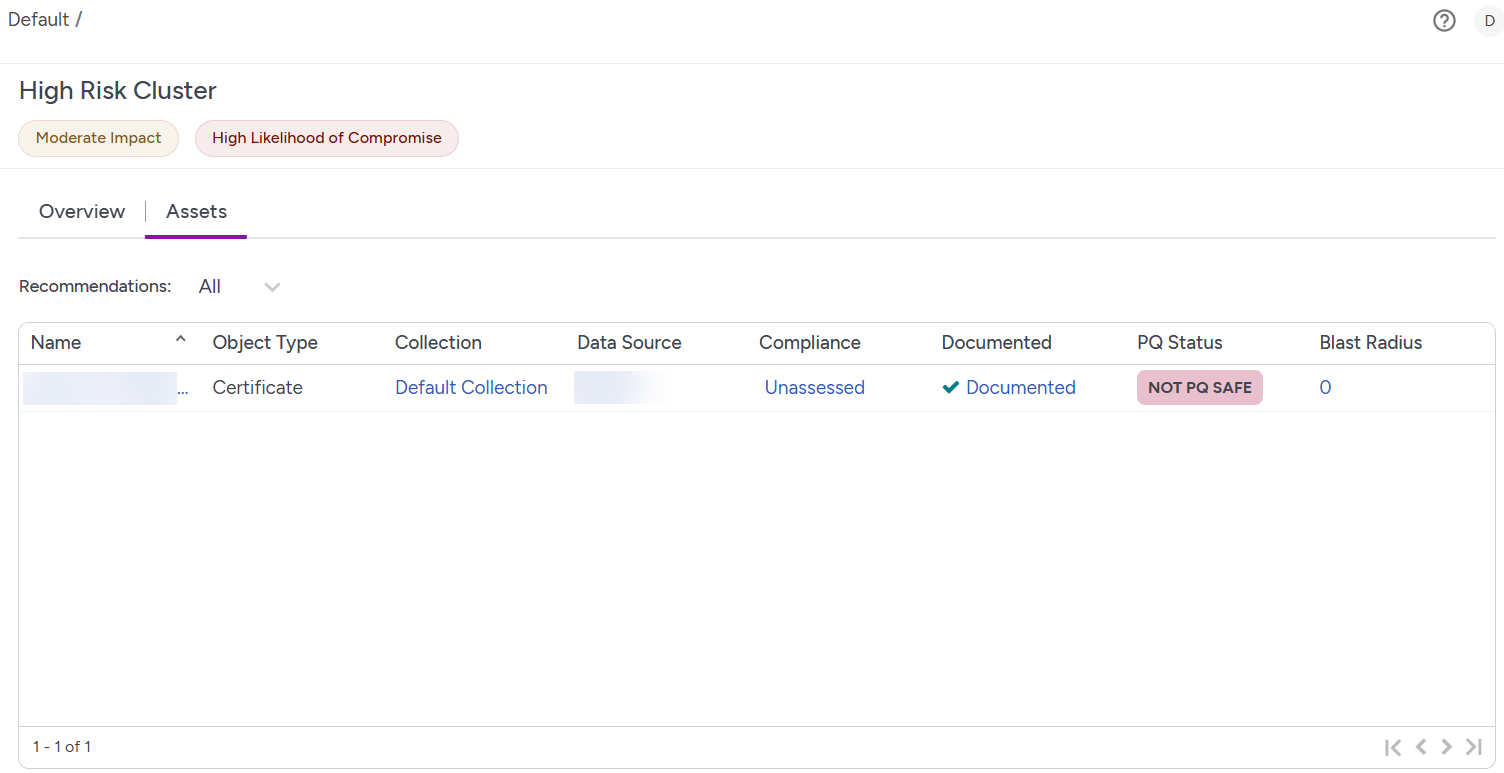
The Security Recommendations page also provides information about the assets within the selected risk category.
Security Recommendations for a Selected Risk Landscape Tile - Assets
Recommendations and Compromise
Security recommendations are derived from the Compromise axis. Compromise represents security conditions that can potentially be remediated.
Impact represents the potential consequences if an asset is compromised and is not directly reduced by remediation activities. For example, moving a private key into an HSM may reduce its likelihood of compromise, but it does not reduce the number of systems that depend on it.
Evaluating Business Impact
Use the Business Impact section to evaluate the potential effect of implementing one or more recommendations before planning a change. Toggle one or more recommendations to evaluate their potential effect on the selected asset.
The Business Impact section displays:
- Total potential risk reduction.
- The number of assets remaining after implementing the security recommendation.
- The number of those assets that remain in production.
- The number of remaining security recommendations found.
- Downstream assets, such as domains, endpoints, and databases.
- The distribution of the assets at risk across countries..
Business Impact for Selected Recommendations
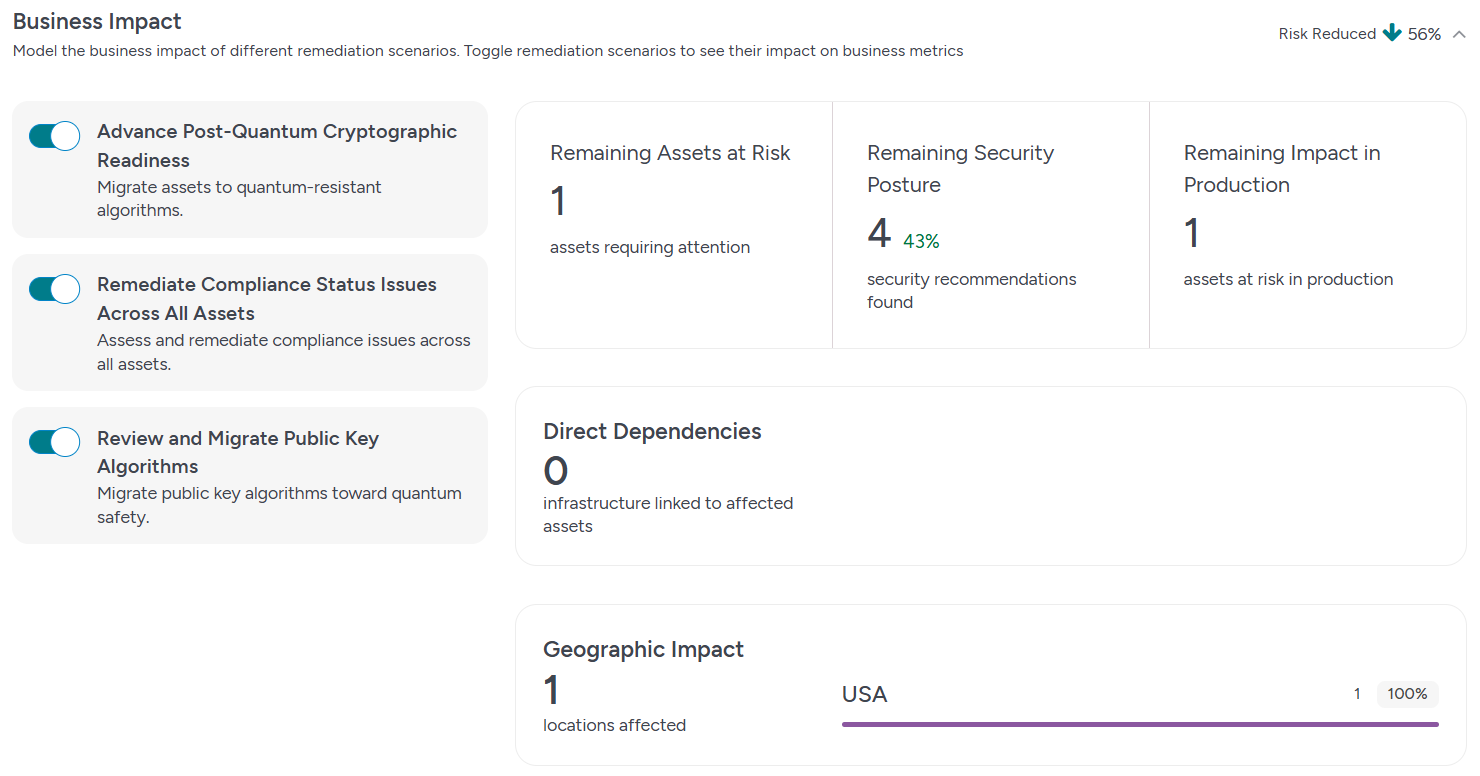
When multiple recommendations are selected, Compliance Manager calculates the combined effect and avoids counting overlapping benefits more than once.
Use Business Impact to compare remediation options and understand their expected risk reduction, production impact, dependencies, and potential blast radius.