In order to deploy the first Cryptographic Security Platform Vault node on AWS, you need to launch a Entrust Cryptographic Security Platform Vault for AWS instance on a new or existing VPC. After you have configured the first Cryptographic Security Platform Vault node, you can add other Cryptographic Security Platform Vault nodes to your Cryptographic Security Platform Vault cluster as desired.
The following procedure is based on the 2019 AWS Console interface. If your version of the AWS Console is different from what is described below, please see your AWS documentation.
To deploy the first CSP Vault node in AWS
- Open a web browser and navigate to the Amazon Web Services login page for your company.
The default login page is https://aws.amazon.com
- Log in to the AWS Management Console with your AWS user name and password.
In the top menu bar just after your login name, verify that the deployment region is correct. If you need to change it, click the current region and select the new region from the drop-down list.
Create a new VPC to use for the Cryptographic Security Platform Vault node, or select an existing VPC.
- In the top menu bar, select Services > Compute > EC2.
- Click the blue Launch Instance button.
- Complete the following wizard steps.
Step 1: Choose an Amazon Machine Image (AMI)
In this page:
- Click AWS Marketplace in the left-hand pane.
Search the Marketplace for "Entrust"
Select Entrust Cryptographic Security Platform Vault for AWS BYOL (Bring Your Own License).
- Review the details
- Click Continue.
Step 2: Choose an Instance Type
In this page, select an instance type. For optimal performance, we recommend that you select a general purpose or compute optimized instance type with SSD Instanced storage, such as:
- m3.large
- c3.large
The Cryptographic Security Platform Vault system resource recommendations are:
Resource | Standard installation | Large installation |
|---|---|---|
CPUs | 2 | 4 |
RAM | 8 GB | 16 GB |
Disk | 65 GB | 150 GB |
Entrust recommends that you select a large installation if your system meets one or more of the following criteria:
- More than four nodes in the Cryptographic Security Platform Vault cluster.
- More than 500 virtual machine heartbeats OR more than 10,000 KMIP keys across all KMIP vaults together.
- More than 100,000 secrets stored.
After you have selected the type, click Next: Configure Instance
Step 3: Configure Instance Details
In this page, configure the following settings.
Number of Instances —Specify the number of instances you want to launch in this field. All instances will run in the same region using the same VPC and instance settings.
You can use this option to create a multi-node Cryptographic Security Platform Vault cluster on this VPC without needing to launch additional instances, but you can also add additional Cryptographic Security Platform Vault nodes to the cluster at any time after the initial node has been configured.
Network —Select the VPC you want to use for the Cryptographic Security Platform Vault node.
- Set all other options on this page according to your corporate standards.
When you are done, click Next: Add Storage.
Step 4: Add Storage page
In this page, configure the following settings.
- Volume Size —Set the size of the disk based on your configuration requirements. The default setting of65 GB should work for most Cryptographic Security Platform Vault installations.
- Volume Type—For optimal performance, we recommend setting the volume type to one of the SSD options instead of the default Magnetic volume.
- Delete on Termination—If you select this option and the instance is deleted, all keys stored on this Cryptographic Security Platform Vault node will be deleted as well. In a single node configuration, this means that encrypted data cannot be decrypted, as the keys will be lost. If you want to use this option, make sure all data is decrypted before the instance is deleted.
When you are done, click Next: Add Tags.
Step 5: Add Tags
In this page, configure the following settings.
- Key —Enter "Name".
- Value—Enter the name for this Cryptographic Security Platform Vault node.
Add any other tags as desired, and click Next: Configure Security Group.
Step 6: Configure Security Group
In this page:
Make sure that the Assign a security group field is set to Create a new security group.
You can use an existing security group as long as all of the required ports are open in that security group.
- Optionally enter a custom security group name and description in the Security group name and Description fields.
- For each of the required entries in the security group, set the Source IP addresses or security groups that can communicate withVault through the associated ports.
We strongly recommend that you do not use the default 0.0.0.0/0 notation, which indicates that the ports are open to the world.
Cryptographic Security Platform Vault requires the following ports:
Type | Protocol | Port Range | Source |
|---|---|---|---|
SSH (22) | TCP | 22 | IP address list or another security group |
HTTPS (443) | TCP | 443 | IP address list or another security group |
Custom TCP Rule | TCP | 5432 | IP address list or another security group |
Custom TCP Rule | TCP | 8443 | IP address list or another security group |
Custom UDP Rule | UDP | 123 | IP address list or another security group |
For details about specifying the source IP addresses or security groups, see your AWS documentation.
When you are done, click Review and Launch.
Step 7: Review Instance Launch
In this page:
- Verify your selections
- Click Launch.
- At the prompt, you can either
- Select an existing key pair
- Select Create a new key pair, specify a key pair name, and download the new private key file for the new key pair.
C click Launch Instances. AWS displays a confirmation page stating that your instance is being launched and displays the instance ID.
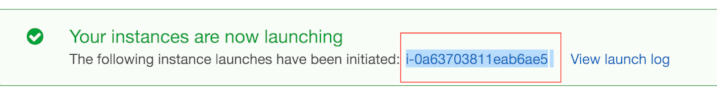
Make a note of the ID, as it will be your initial Cryptographic Security Platform Vault password.
Select Services > EC2 > Instances, locate the new instance in the table and verify the status.
If you requested multiple instances on the Step 3: Configure Instance Details page, you will see multipleVault instances with the same name listed in the table. We recommend that you give each instance a unique name at this point so that you can tell them apart as you configure them (mouse over an instance name and click the pencil icon when it appears).